The practice
Who is behind Ruvalin
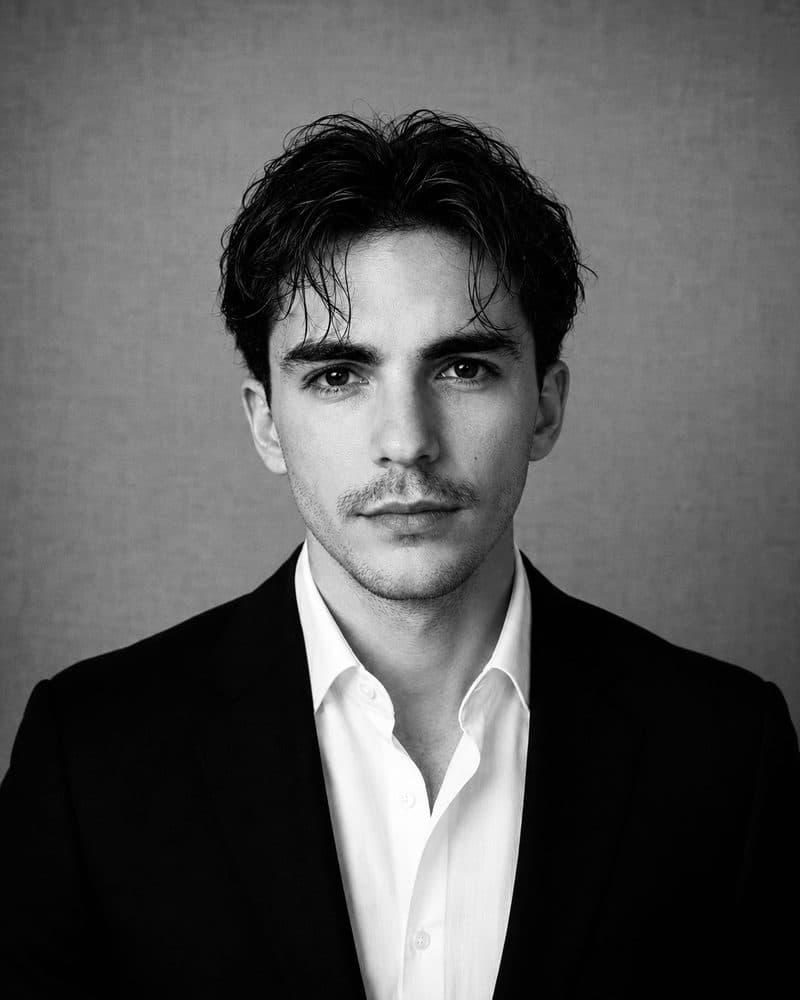
Ruvalin is the practice of Tom Gernez, an independent information security consultant based in Montigny-lès-Metz, France. It sets up email authentication for small firms and professional practices, monitors it, and trains their staff against phishing. You will speak to the same person from the first call through to the final report.
The background
Tom Gernez, French independent information security consultant. Ruvalin is a sole trader registered in France; the full legal identity, address and registration number are in this site's legal notice. That is not a formality: it is the difference between a supplier you can place on a map and a contact form.
Engagements involving penetration testing are delivered together with senior partner engineers, under my responsibility. Everything else I do myself: the audit, the configuration, the reading of the reports, the training.
How I work
The method is the same on every engagement, and it is published here in full. There is nothing to discover along the way.
- 01
A fifteen-minute call
We look at your domain name together, during the call. Fifteen minutes later you know whether you are exposed, and you know it whether or not we go on to work together.
- 02
The audit
One hour. It relies only on the public DNS records of your domain, the ones anyone can look up. No access to your systems is needed, and the same audit is available to run yourself on this site.
- 03
The remediation
Half a day. I hand you the exact values to enter with your hosting provider. You can apply them yourself or give me limited access to the DNS zone. Never to your mailboxes.
- 04
The rollout
Two to three weeks, almost entirely on my side. We stay in monitoring until every service legitimately sending in your name has been identified, then tighten in stages. The full procedure is published in the guide on moving to rejection.
- 05
The monitoring
After that, a monthly summary in plain language: who tried to impersonate your domain, what was rejected, and what needs adjusting when you change tools.
Three principles
- No black box. The record I publish on your domain is written out in full on the home page, with every part of it translated. What I do is checkable by a third party, and it should be.
- No access I do not need. The initial audit reads only public DNS. The implementation needs the DNS zone, and nothing else. A mail system is not secured by logging into it.
- No unverifiable numbers. You will find no client logos here, no testimonials and no percentages. Discretion is part of the work, and I would rather be judged on what I say on the phone.
What I do not do
A short list, because it will save you a call if your need is elsewhere.
- I do not sell software, and I do not resell a third party's platform at a margin. The tools published on this site are free and will stay free.
- I do not do managed IT, general helpdesk or backup. If your problem is a laptop, I am not the person to call.
- I do not take penetration testing work without a written mandate and a defined scope. That is a legal requirement as much as a professional one.
- I do not promise that a configuration stops all fraud. What domain authentication stops, and what it lets through, is set out plainly in the guides.
Identity
- Legal name
- Tom Gernez
- SIRET
- 947 978 433 00037
- Activity code
- 6202A
Getting in touch
The phone is still the quickest route. Fifteen minutes is enough to establish whether your domain is exposed, and the call commits you to nothing.
- Telephone
- +33 6 44 64 17 13
- contact@ruvalin.com